As security vendors form AI coalitions with model providers, cloud companies, and service firms, buyers need to know who controls the data, decisions, and systems that follow.
As security vendors form AI coalitions with model providers, cloud companies, and service firms, enterprises have more options for securing AI systems. But they also face a basic question: who controls the data, decisions, and systems involved?
These coalitions can bring together AI models, security tools, implementation expertise, and managed services. But buyers still need to understand how those capabilities fit into their existing environment—and who is responsible when something goes wrong.
For financial services and insurance organizations, that means looking closely at data flows, permissions, accountability, and operational control before adopting a coalition-backed solution. An alliance announcement doesn’t define the organization’s architecture, operating model, or control framework. A delivery partner should help the enterprise determine what data will move between participants, how permissions will be enforced, which controls remain enterprise-owned, and who’ll operate the system.
Why AI security coalitions are forming
AI is changing both sides of cybersecurity. Security teams can use models to analyze code, identify attack paths, prioritize vulnerabilities, investigate alerts, and support incident response. Attackers can use AI to automate reconnaissance, tailor phishing, discover weaknesses, and accelerate malicious activity.
That creates a need to connect model capabilities with security data, identity controls, cloud telemetry, incident response, software-development processes, and human decision-making. Those requirements span technologies and responsibilities that aren’t necessarily supplied by one vendor.
How vendors are organizing AI security
CrowdStrike, Palo Alto Networks, and NVIDIA demonstrate three related approaches to AI-security collaboration. CrowdStrike is organizing a coalition around AI-assisted vulnerability discovery and remediation. Palo Alto Networks is combining its security platform with consulting and managed-service partners. NVIDIA is supporting an open ecosystem for shared tools and defenses intended to work across vendors and infrastructure environments.
CrowdStrike: AI vulnerability discovery and remediation
Courtesy of CrowdStrike, 2026.
Project QuiltWorks is CrowdStrike’s coalition for assessing, prioritizing, and continuously remediating vulnerabilities identified with frontier AI capabilities. The initial coalition included Accenture, EY, IBM Cybersecurity Services, Kroll, OpenAI, CrowdStrike, and its broader partner ecosystem, with frontier models from OpenAI and Anthropic supporting the work.
CrowdStrike later expanded Project QuiltWorks with additional systems integrators, technology partners, cyber-insurance participants, and AWS. The broader model now combines AI-assisted discovery and prioritization with partner-led remediation, cloud hardening, NVIDIA Nemotron models, and financial-risk support.
AI-assisted discovery can produce more potential findings than an internal team can validate, prioritize, and remediate at once. However, faster discovery doesn’t remove the harder work of deciding which findings are credible, material, exploitable, and worth fixing first.
CrowdStrike has also expanded its relationship with OpenAI to extend Falcon Guardian security to supported Codex agents and bring GPT-5.6 Cyber to the Falcon platform. That connects agent inventory, runtime visibility, activity controls, cyber reasoning, and risk-assessment workflows more closely.
Palo Alto Networks: security platforms and managed delivery
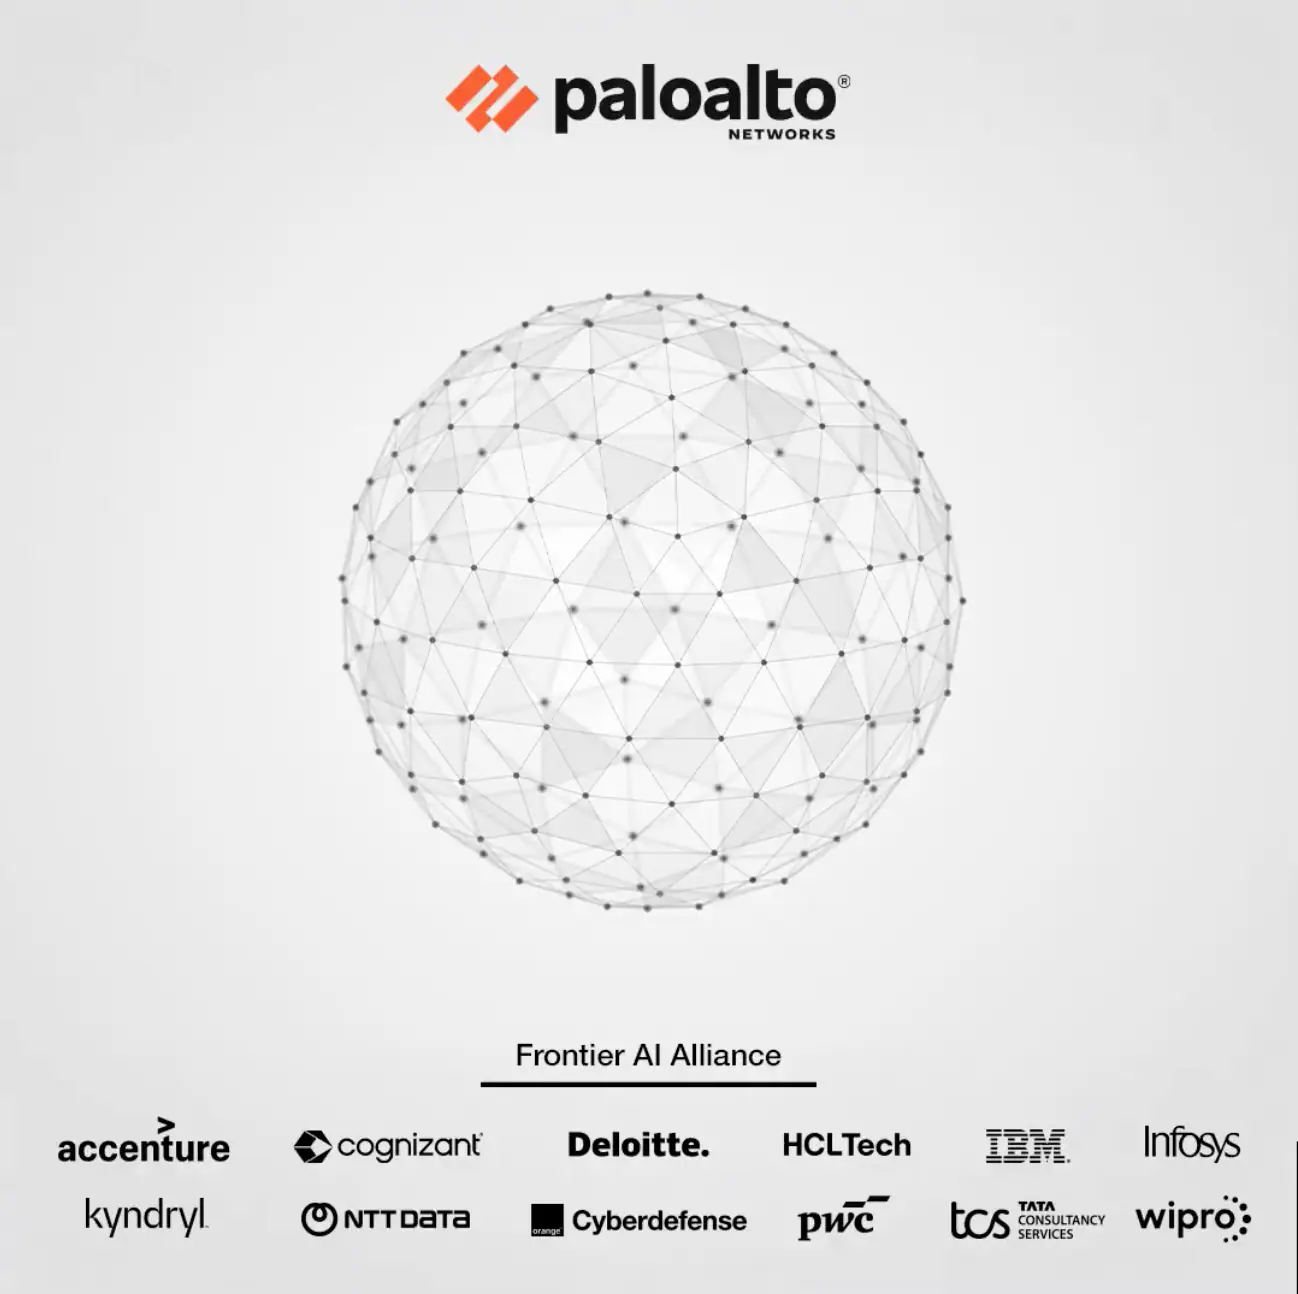
Courtesy of Palo Alto Networks, 2026.
Palo Alto Networks is taking a platform-and-services approach to AI security. Its Frontier AI Alliance brings its security technology together with consulting and managed-service partners, including Accenture, Deloitte, IBM, NTT DATA, and PwC. The alliance later added Cognizant, HCLTech, Kyndryl, TCS, Infosys, McKinsey & Company, Orange Cyberdefense, and Wipro.
Its alliance with NTT DATA combines Palo Alto Networks’ security platforms with NTT DATA consulting, engineering, AI governance, and managed services. The initial offerings include autonomous security operations, identity security, zero trust, and resilient cloud services, with financial services among the regulated sectors the companies identify as a priority.
Palo Alto Networks and its partners position the alliance as a way to give enterprises a more direct path from AI-security assessment to implementation and remediation. Whether it reduces procurement or delivery complexity will depend on the organization’s existing platforms, contracts, and operating model.
NVIDIA: open tools and cross-vendor defenses
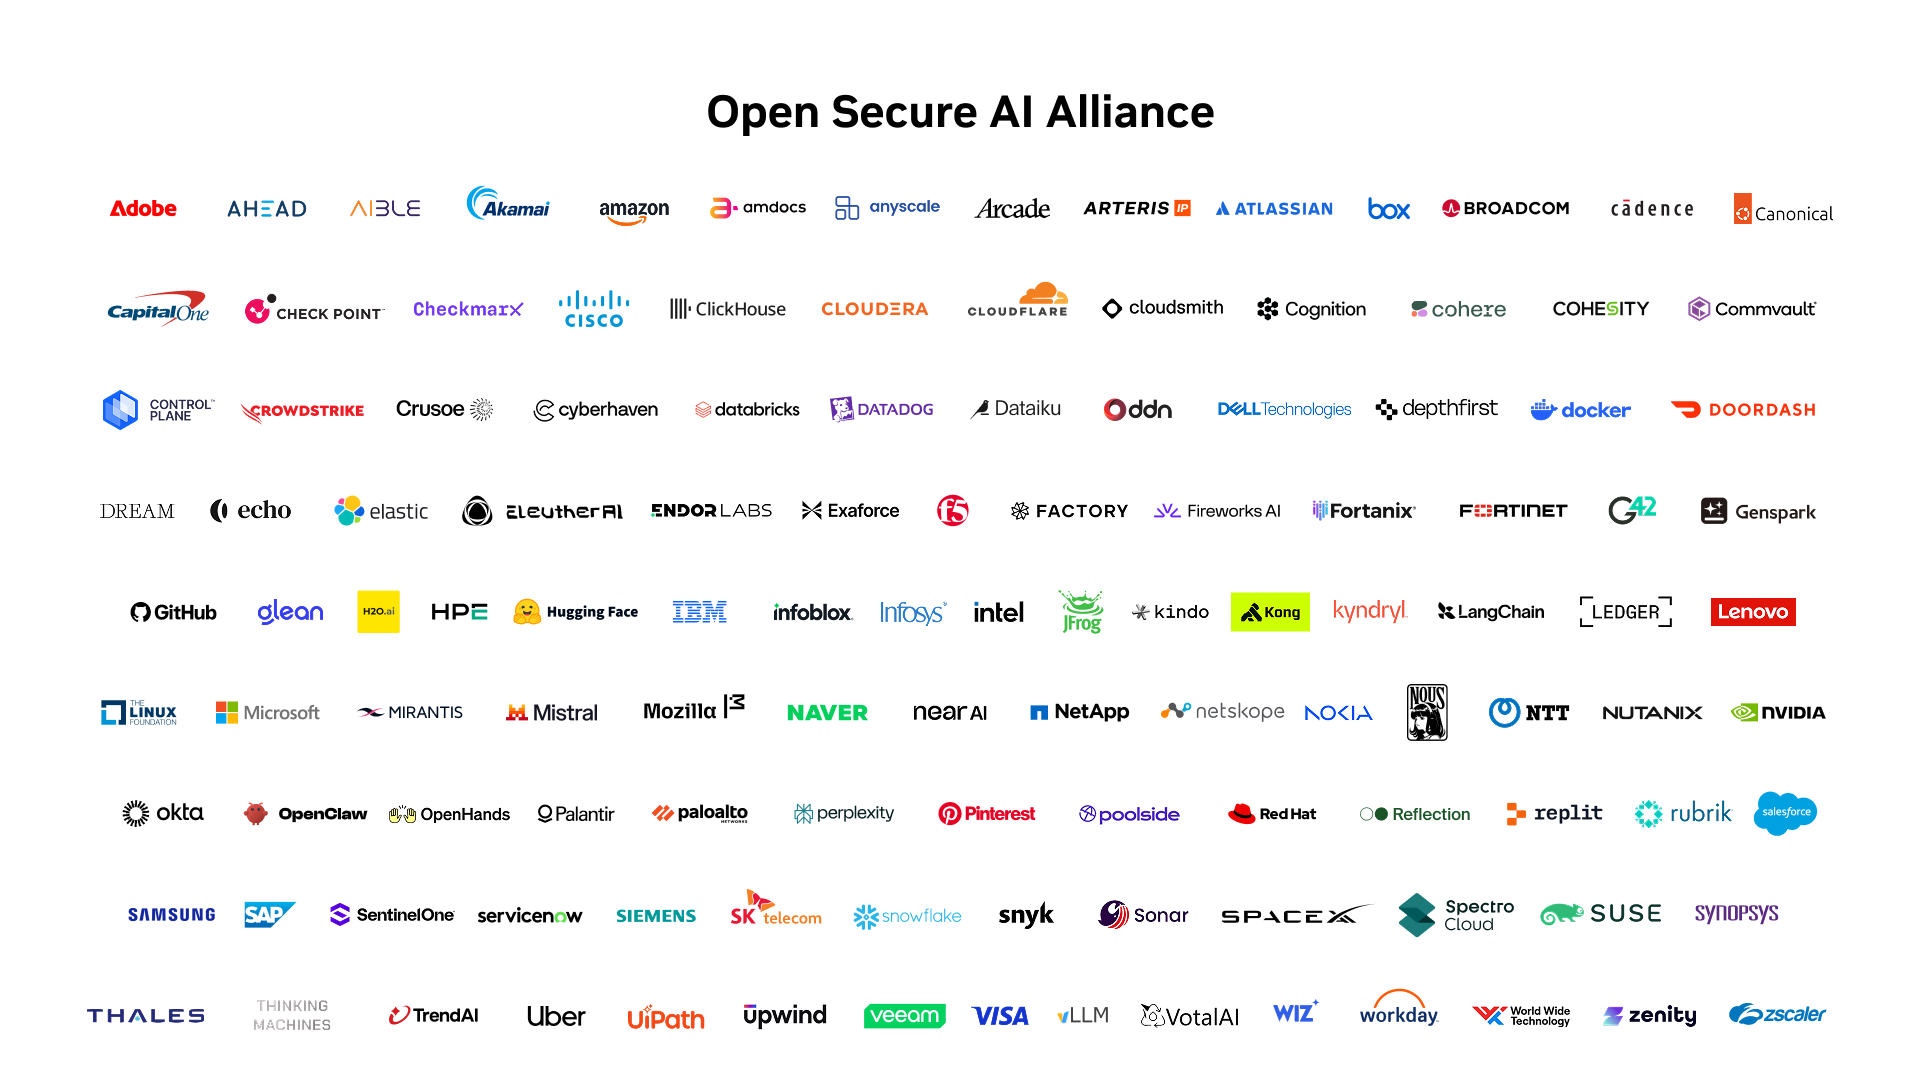
Courtesy of NVIDIA, 2026.
NVIDIA launched the Open Secure AI Alliance in July 2026 to develop and share open technologies for securing AI systems, software, and agents. The alliance brings together organizations across cybersecurity, cloud infrastructure, enterprise software, financial services, and open source, including CrowdStrike, Palo Alto Networks, Capital One, Visa, Hugging Face, Microsoft, IBM, Salesforce, SAP, ServiceNow, and the Linux Foundation.
The alliance is developing an open defense stack intended to support agent identity, isolation, secure model formats, vulnerability scanning, secure software development, and shared threat intelligence. In September 2026, the alliance joined the Linux Foundation, which described the move as a way to build a shared, open defense stack for the AI era.
What changes for regulated buyers
Enterprises aren’t choosing whether to form an AI-security coalition. They’re deciding whether a coalition-backed product or service fits their existing security environment. That assessment should account for the organization’s technology stack, internal engineering capacity, data-handling requirements, cloud environment, risk appetite, and need for operational control.
Banks, insurers, payment providers, and other regulated organizations already manage risk, access control, third-party oversight, resilience, incident response, and evidence retention. Coalition-backed AI-security offerings don’t replace those responsibilities. However, depending on how they’re implemented, coalition-backed offerings can introduce additional technology, data, and operating dependencies that have to fit into the existing control environment.
Data use and confidentiality
A coalition-supported workflow may involve source code, software-bill-of-materials data, cloud configurations, security logs, model prompts, or incident information. Buyers should know whether that data stays within their environment, is processed by a vendor, is retained after the engagement, or is used to improve a model or service.
The answer may differ among the security vendor, model provider, delivery partner, and managed-service provider. A partner should map those flows before implementation and align them with internal data-classification rules, customer commitments, contractual requirements, and applicable regulations.
Identity and agent actions
AI systems and security agents should receive only the access required for their approved tasks. A workflow may need to read alerts, retrieve configuration data, open tickets, trigger containment actions, or recommend remediation. Each agent needs a defined identity, narrowly scoped permissions, and activity logging, with human approval for higher-impact actions.
The organization should know which system authorizes an action, how permissions are enforced across connected tools, and how the workflow responds when an agent encounters an exception.
Ownership and accountability
In a coalition-backed service, responsibilities may be divided among a model provider, security vendor, systems integrator, cloud provider, and managed-service provider. A model provider may provide reasoning capabilities, a security vendor may provide the platform and telemetry, a systems integrator may configure the workflow, and a managed-service provider may monitor the environment.
The enterprise still needs an operating model that assigns responsibility for configuration, model changes, access reviews, alert triage, remediation, incident response, audit evidence, vendor escalation, and service performance. Those responsibilities should be documented before the AI-supported control enters production.
An AI security coalition is a partnership among cybersecurity vendors, AI model providers, cloud companies, systems integrators, and other organizations working on tools and services for securing AI systems. These coalitions may combine vulnerability discovery, threat intelligence, cloud security, agent controls, remediation services, and open security tooling. CrowdStrike’s Project QuiltWorks, for example, combines AI-assisted vulnerability discovery with partner remediation services and cloud infrastructure support.
Why should enterprises evaluate AI security coalitions carefully?
A coalition announcement does not define how a product or service will fit into an enterprise environment. Buyers should assess data flows, identity and access controls, integration requirements, service ownership, logging, incident response, commercial terms, and the long-term effect of dependencies on their technology stack.
What should financial services and insurance firms ask about AI security partners?
Financial services and insurance organizations should ask how a coalition-backed offering handles customer data, access controls, audit rights, evidence retention, vendor oversight, incident reporting, and regulatory cooperation. Federal banking guidance emphasizes documented incident processes, accountability, timely escalation, and access to data and supporting documentation in third-party arrangements.
How should AI agents be governed in a security workflow?
Each AI agent should have a distinct identity, narrowly scoped permissions, activity logging, and a defined owner. Lower-risk actions—such as enriching alerts or drafting tickets—may be automated, while higher-impact actions, such as changing access controls or containing systems, should have clear review and approval requirements. NIST’s AI Risk Management Framework calls for defined roles, responsibilities, monitoring, incident-response processes, and oversight for AI systems.
What should a delivery partner document before implementing an AI security service?
Before implementation, a delivery partner should document the proposed architecture, connected systems, data categories, identities and permissions, model and vendor dependencies, security controls, approval paths, operational ownership, incident-response responsibilities, monitoring requirements, change-management processes, and exit options. This gives the enterprise a practical record of what it is adopting, who operates it, and what changing providers would require.
AI is changing software development.
The Engineer's AI-Enabled Development Handbook is your guide to incorporating AI into development processes for smoother, faster, and smarter development.
Enjoyed the article? Get new content delivered to your inbox.
Subscribe below and stay updated with the latest developer guides and industry insights.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.
We use cookies to provide our services, to allow us to better understand our audience, and to provide and serve personalized ads or content. By using our website, you consent to the terms of our Privacy Policy and our Cookie Policy, and the use of cookies, pixels, and other technology as described more fully therein
The GPC signal has been honored.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.